

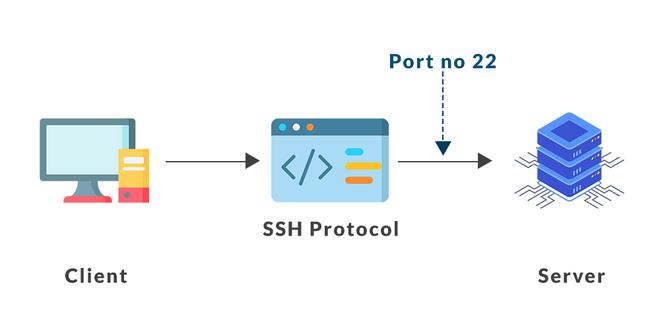
SFTP (SSH File Transfer Protocol, also called Secure File Transfer Protocol) is a secure network protocol used to transfer files between computers. Unlike FTP, it encrypts all data and commands. It runs over SSH(Secure Shell), uses port 22 by default, and follows the client-server model.
Features
- Encrypts data during transfer, so it can't be read if intercepted.
- Lets users run commands on the remote server.
- Compresses data to speed up transmission.
- Supports username and password authentication.
- Makes uploading and downloading files faster and smoother.
- Supports public key authentication for a more secure login.
Working
SFTP works on top of SSH. First, the client connects to the server and a secure, encrypted channel is set up. The server is then verified, and the user logs in with a password or a public key. Once that's done, all commands and file data travel through this encrypted channel, and a Message Authentication Code (MAC) is added to each data packet to make sure it isn't altered on the way. If an unauthorized person or third party intercepts the data, all they get is unreadable, scrambled text.
For example, just like WhatsApp messages are end-to-end encrypted, so only the sender and receiver can read them, SFTP keeps file transfers private between the client and the server.
Advantages
Speed and Efficiency: SFTP can handle large files without trouble, transferring them in a single session. Data moves quickly and with little overhead.
Lower risk while exchanging data: SFTP sends data in encrypted form, so unauthorized people can't read it. It also verifies the server's identity (host authentication), so you know you're connecting to the right server and not a fake one.

Easy data access: SFTP makes data easy to reach. You can transfer files from a user's system to a server, and also directly from one server to another.

Disadvantages
Difficult to manage: SFTP can be harder to set up and maintain. Managing SSH keys, user permissions, and server configuration takes extra effort, especially on larger systems.
Security risks from misconfiguration: SFTP is secure by design, but it is not immune to attacks. Weak passwords, poor SSH configuration, or compromised credentials can still expose the server to cyber attackers.
Configuration of SFTP
Configuration of SFTP for Windows
- SSH is preinstalled on most versions of Windows. If it isn't, install OpenSSH first (Settings > Apps > Optional features).
- Open the Control Panel and search for "Windows Defender Firewall", then click on "Advanced settings".
- In the window that opens, click on "Inbound Rules".
- Click on "New Rule" in the right-hand panel and allow port 22.
- Finally, choose an SFTP client. Commonly used ones on Windows are WinSCP, FileZilla and Cyberduck.
Configuration of SFTP for macOS
- SSH comes preinstalled on all Macs.
- To allow the SFTP port, open the firewall settings: System Settings > Network > Firewall (older versions: System Preferences > Security & Privacy > Firewall > Firewall Options).
- FileZilla and Cyberduck can be used as SFTP clients.
Configuration of SFTP for Linux
- To install SSH on Ubuntu, run
sudo apt install sshin the terminal. - To allow SFTP port 22, run
sudo ufw allow ssh. - FileZilla and many other open-source clients are available for Linux.
How to secure an SFTP server
- Use a strong password with capital letters, small letters, numbers and special characters. Example:
Geeks123_45#@$Cn# - Monitor the account regularly. If you notice any unusual activity, inform your administrator and change the password immediately.
- Use strong encryption algorithms.
- Set proper file permissions to protect your data.
- Restrict access using blacklists and whitelists.
