

A Docker Repository is a collection of related Docker images stored under the same repository name. Different tags are used to identify specific versions of an image.
- Repository groups related images, such as
ubuntuornginx. - Tags identify different image versions, such as
:20.04or:latest. - Example like
nginx:latestrefers to thenginxrepository with thelatesttag.
Docker Hub
For most developers, Docker Hub is the default and largest public registry. It serves as a vast storage area for millions of Docker images. It provides services like automated builds, security scanning, and both public and private repositories.
Docker Image Naming Convention
Before pushing or pulling images, it's essential to understand how they are named. The full name of a Docker image follows a specific format:
[registry_hostname/][username/]<image_name>[:<tag>]| Component | Meaning | Example |
|---|---|---|
| Registry Hostname (Optional) | Registry where the image is stored. Defaults to Docker Hub if omitted. | docker.io |
| Username (Optional) | User or organization that owns the repository. | bitnami |
| Image Name (Required) | Name of the Docker image/repository. | mongodb |
| Tag (Optional) | Specifies the image version. Defaults to latest if omitted. | :1.0.1, :18-alpine |
Image Types on Docker Hub
| Image Type | Maintained By | Example | Key Point |
|---|---|---|---|
| Official Images | Docker | ubuntu, nginx, redis | Trusted and follow best practices |
| Verified Publisher Images | Trusted companies | Microsoft, Oracle, Bitnami | Published by verified vendors |
| User Images | Docker community | username/image_name | Quality and security may vary |
Private Registries
- Internal Distribution: Share Docker images within your company without using the internet.
- Faster CI/CD: Push and pull images faster within your own network.
- Large Deployments: Easily deploy images across multiple servers or devices.
- Better Storage Control: Keep and manage images within your own infrastructure.
How to choose Right Container Registry
- Know Your Needs: Identify the features you require in the register. Which should you prefer—on-site or in the cloud? What features are required for your procedure?
- Check Features: Essential characteristics to look for include access control, security scanning, and interaction with current tools. Select a registry which has the features you require.
- Security First: Ensuring that security and compliance come first in the registry. Check for encryption, access controls, and compliance to regulations such as HIPAA and GDPR.
Docker Repository
A Docker repository is a collection of different Docker images with the same name, that have different tags. Tags basically are identifiers of the image within a repository. In this tutorial, we will use Docker Hub to host our repositories, which is free for public use.
Step 1: Creating An Account On Docker Hub. Go to DockerHub and create a new account or log in to your existing account.

Step 2: Creating A Repository (optional)
On the docker hub, you can create a repository by clicking on create repository button. Give the repository a name and description and make sure it is marked as public. This step is not necessary when you are hosting a public repository. It is used while hosting a private one.
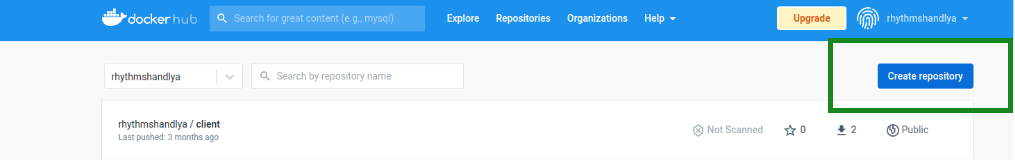
Repository Name image widget.
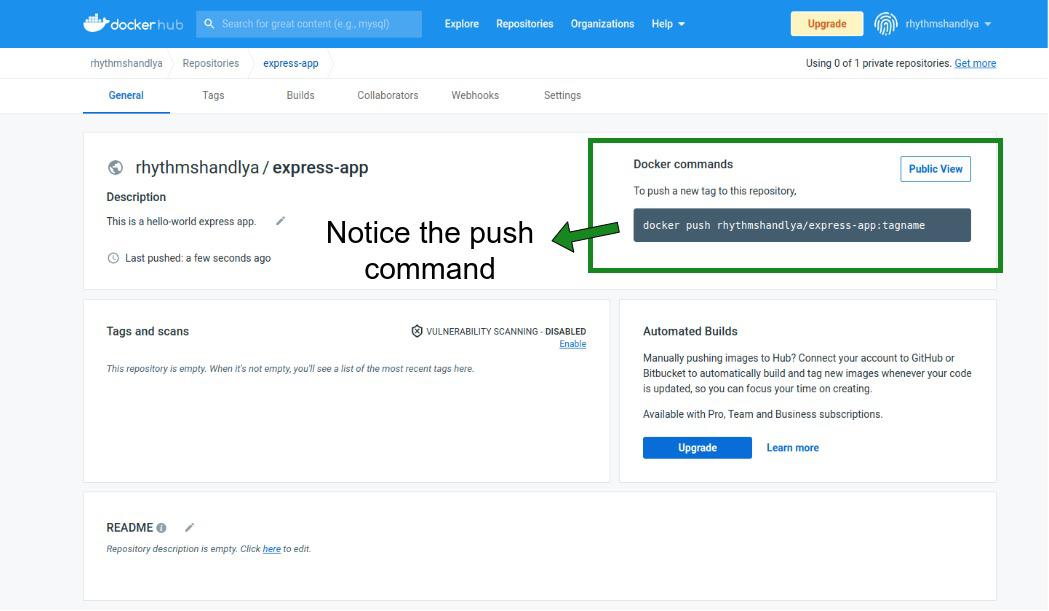
Step 3: Build a Docker Image
Now we will generate a basic express application and create an Image out of it.
$ mkdir express-app && cd express-app
$ npx express-generator -e

Now, create a Dockerfile for the application and copy the content as shown below:
$ touch DockerfileFROM node:16
# Create app directory
WORKDIR /usr/src/app
# Install app dependencies
# A wildcard is used to ensure both package.json
# AND package-lock.json are copied
# where available (npm@5+)
COPY package*.json ./
RUN npm install
# If you are building your code for production
# RUN npm ci --only=production
# Bundle app source
COPY . .
EXPOSE 3000
CMD [ "npm", "start" ]

You can now build this Dockerfile with the docker build command.
$ docker build -t rhythmshandlya/express-app .
One thing to notice is as did not specify the tag name, it will be given the : latest tag.
Step 4: Run This Image Locally.
$ docker run -p 3000:3000 rhythmshandlya/express-app
Step 5: Push Image to docker hub. To push a local Image to the docker hub we will need to log in to the docker hub with our terminal.
$ docker login
$ docker push rhythmshandlya/express-app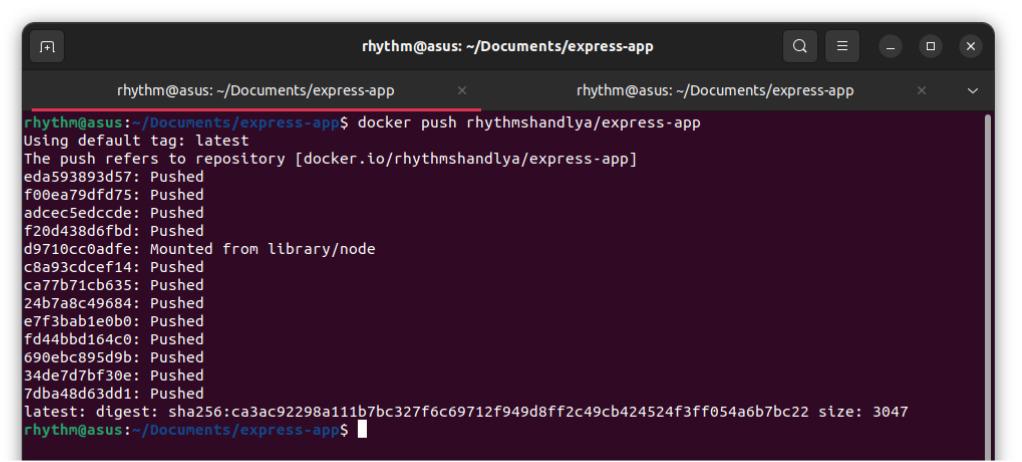

Step 6: Playing With Tags. We can make changes to this application and give it a version tag of 0.0.1
$ docker build -t rhythmshandlya/express-app:0.0.1 .
$  docker push rhythmshandlya/express-app:0.0.1
Output:
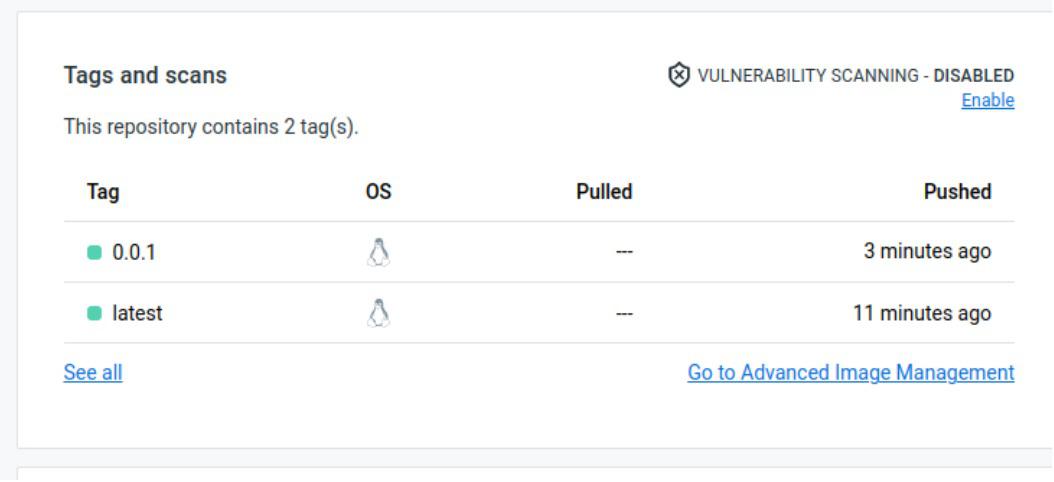
Now that we have hosted our image in public anyone can pull and run them on their machines.
$ docker pull rhythmshandlya/express-app:latest
OR
$ docker push rhythmshandlya/express-app:0.0.1
Different Container Registries
Amazon Elastic Container Registry (ECR)
Amazon ECR is a fully managed container registry service provided by AWS for storing and managing container images. It integrates with AWS services such as ECS and EKS for deploying containerized applications.
- Image Management: Provides lifecycle policies to manage images.
- Security: Supports image scanning and encryption at rest.
- AWS Integration: Works seamlessly with ECS, EKS, and other AWS services.
Google Container Registry (GCR)
Google Container Registry (GCR) is Google Cloud's managed service for storing and managing container images. It integrates with GKE and other GCP services to support containerized application deployment.
- Vulnerability Scanning: Supports scanning through Container Analysis.
- Access Control: Uses IAM roles to manage access.
- Automated Builds: Integrates with Google Cloud Build for automated image builds.
- GCP Integration: Works with GKE and other Google Cloud services.
Azure Container Registry (ACR)
Azure Container Registry (ACR) is Microsoft's managed container registry service for storing and managing container images. It integrates with AKS and other Azure services for containerized application deployment.
- High Availability: Supports geo-replication for availability across regions.
- Access Control: Provides role-based access control (RBAC) with Azure Active Directory.
- Image Security: Supports image signing with Docker Content Trust.
- Azure Integration: Works with AKS and other Azure services.
Harbor
Harbor is an open-source container registry designed for secure storage and management of container images. It can be deployed on-premises or in the cloud and integrates with Kubernetes, Docker, and other container technologies.
- Access Control: Provides role-based access control (RBAC).
- Image Security: Supports vulnerability scanning and image policies.
- Image Replication: Allows images to be replicated across registries.
- Deployment: Can run on-premises or in the cloud.
GitLab Container Registry
GitLab Container Registry is integrated with GitLab's CI/CD pipelines, allowing developers to build, test, and deploy containerized applications within the same platform.
- CI/CD Integration: Works directly with GitLab CI/CD pipelines.
- Container Scanning: Provides built-in scanning for container images.
- Access Control: Uses project-level permissions to manage access.
- Image Versioning: Supports managing different versions of container images.
JFrog Artifactory
JFrog Artifactory is an artifact repository manager that supports Docker images and other package formats such as Maven, npm, and NuGet.
- Replication: Supports replicating artifacts across repositories.
- Access Control: Provides controls for managing user access.
- Metadata Management: Stores and manages artifact metadata.
- Search: Provides advanced search capabilities for finding artifacts.
