

DNS caching temporarily stores previously resolved DNS records so that future queries can be answered faster without repeating the complete DNS resolution process. It reduces lookup latency, DNS traffic, and load on upstream DNS servers.
- Stores recently resolved DNS information for reuse until its cache lifetime expires.
- Reduces repeated DNS queries and improves domain-resolution performance.
Example: When you visit www.geeksforgeeks.org, its DNS information may be cached. If the same domain is requested again while the cached record is still valid, the result can be reused instead of performing the complete DNS lookup again.
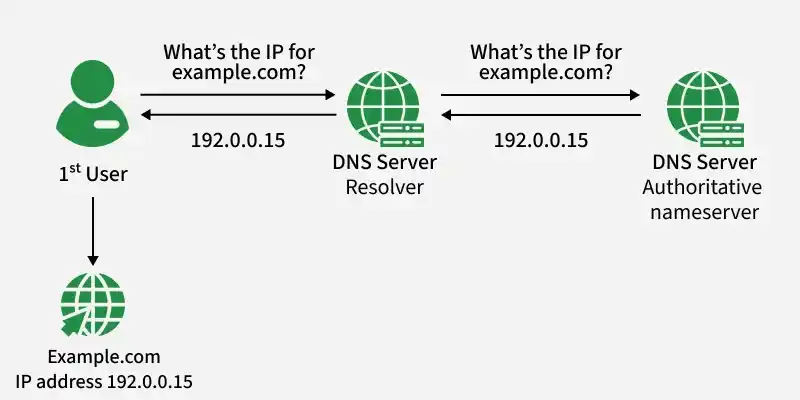
When a domain is resolved for the first time, a recursive DNS resolver may need to query multiple DNS servers to obtain the required record. The result can then be cached according to its TTL so that subsequent queries can be answered more quickly.
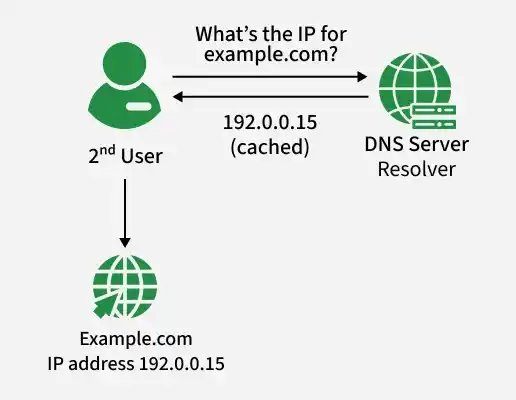
How DNS Caching Works
DNS caching allows previously resolved DNS information to be reused until it expires.
A typical flow is:
- Client Request: An application requests a domain such as example.com.
- Local Cache Check: The browser or operating system checks whether a valid cached DNS record is available.
- Recursive Resolver Query: If the record is not available locally, the client sends a query to a recursive DNS resolver.
- Resolver Cache Check: The resolver checks its own cache.
- DNS Resolution: If the required information is not cached, the resolver may query root, TLD, and authoritative name servers as needed.
- Cache Storage: The returned DNS records may be cached according to their TTL values.
- Final Response: The resolver returns the result to the client.
- Subsequent Requests: Later requests can use valid cached records without repeating the complete resolution process.
Levels of DNS Caching
DNS caching occurs at multiple levels to reduce lookup time and unnecessary DNS queries. Each level checks for valid cached records before proceeding to the next step.
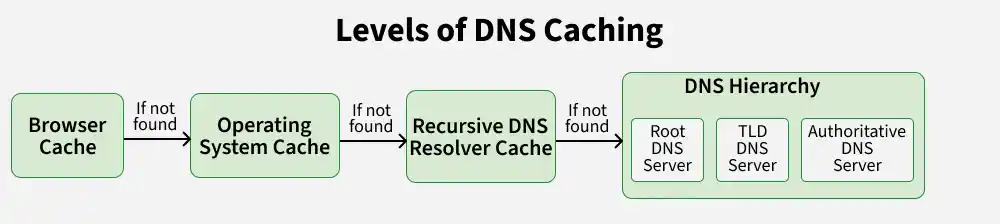
- Browser Cache: Some browsers store recently resolved DNS information to avoid repeated lookups for the same domain.
- Operating System Cache: Stores DNS records locally, allowing applications to reuse valid results without contacting an external resolver.
- Recursive DNS Resolver Cache: Caches DNS responses from previous queries. If a valid record is unavailable, the resolver performs additional DNS lookups.
- DNS Hierarchy: When required information is not cached, the recursive resolver queries Root, TLD, and Authoritative DNS servers as needed to resolve the domain.
TTL (Time to Live) in DNS Caching
TTL specifies how long a DNS record may remain cached before it is considered expired.
TTL values are measured in seconds and are provided with DNS records by authoritative DNS infrastructure.
How TTL Works
- A DNS response contains a TTL value.
- The cache stores the record and tracks its remaining lifetime.
- While the TTL remains valid, the cached record can be reused.
- After expiration, the cached entry is no longer considered valid and a fresh lookup may be required.
Example: If a DNS record has a TTL of 3600 seconds, it can generally remain cached for up to one hour before it expires.
Benefits of DNS Caching
DNS caching improves name resolution speed, reduces network traffic, and supports efficient DNS operations. Key benefits include:
- Faster DNS Resolution: Returns valid cached records without repeating the complete DNS lookup process.
- Reduced Network Traffic: Minimizes unnecessary DNS queries by reusing cached responses.
- Reduced DNS Server Load: Decreases repeated requests to root, TLD, and authoritative name servers.
- Improved Application Performance: Reduces DNS lookup delays, helping websites and applications establish connections faster.
- Better Scalability: Distributes DNS query workloads across multiple caching layers, reducing pressure on authoritative DNS infrastructure.
Best Practices for DNS Caching
Effective DNS caching requires balancing performance, reliability, and data freshness. Key best practices include:
- Set Appropriate TTL Values: Use longer TTLs for stable DNS records and shorter TTLs for records that change frequently.
- Rely on TTL-Based Expiration: Allow DNS records to expire automatically based on their TTL instead of unnecessarily flushing caches.
- Flush Cache When Troubleshooting: Clear DNS caches when stale or incorrect records cause resolution issues.
- Plan TTL Changes Before DNS Migrations: Reduce TTL values in advance so cached records expire sooner during DNS updates.
- Use Reliable Recursive Resolvers: Choose dependable DNS resolvers with redundancy to minimize resolution failures and improve availability.
DNS Cache Security
DNS caching can be targeted by attacks that attempt to insert forged or incorrect records into resolver caches.
- Cache Poisoning Protection: Resolvers should use secure implementations, randomized transaction IDs and source ports, and other validation mechanisms to reduce forged responses.
- DNSSEC Validation: DNSSEC uses digital signatures to verify the authenticity and integrity of signed DNS data.
- Resolver Hardening: Recursive resolvers should be kept updated and configured to reject invalid or suspicious DNS responses.
